- [email protected]
- Innovation One, DIFC, Dubai
Blog
Beyond the Firewall: The Stealthy USB Attack That Bypassed Modern Defenses
Beyond the Firewall: The Stealthy USB Attack That Bypassed Modern Defenses
In the ever-evolving landscape of cybersecurity, we often focus on the digital battlegrounds: phishing emails, network intrusions, and zero-day exploits. But what happens when the enemy bypasses all of that by simply walking into the room? A recent, chilling report from CrowdStrike details a sophisticated attack campaign by China-linked hackers, dubbed OVERCAST PANDA, that leveraged physical access and a seemingly innocuous USB drive to compromise high-profile executives. This wasn't a breach of firewalls or a hack of online credentials; it was an 'evil maid attack' executed with state-sponsored precision.
The "Evil Maid" Strikes Back
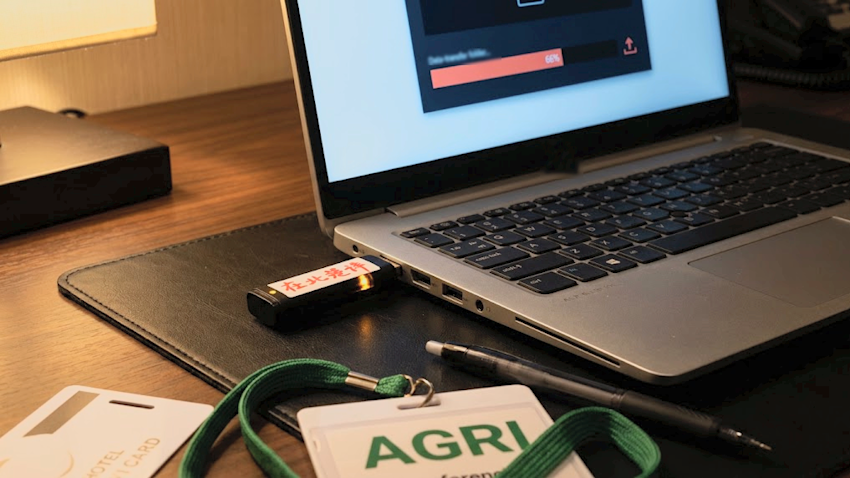
Imagine this: you're at an international conference, staying in a hotel. You leave your laptop in your room for a few hours while you attend a dinner. When you return, everything seems fine. But while you were away, an intruder entered your room, plugged a USB drive into your unattended laptop, installed malware, and then discreetly rebooted your machine. This is precisely what happened to executives attending an agricultural conference in China. The malware, known as FlowCloud, lay dormant, waiting for the next boot-up to activate keylogging, screen capture, and credential harvesting.
What makes this attack particularly alarming is how it sidestepped traditional security measures. According to CrowdStrike's findings, there was:
- No network intrusion: The attackers didn't need to breach any network perimeters.
- No phishing emails: Victims weren't tricked into clicking malicious links or downloading files.
- No stolen credentials: No login pages were compromised.
This attack operated at a layer below most conventional security tools, including endpoint detection and response (EDR) solutions and multi-factor authentication (MFA), which rely on the operating system being loaded and active.
A Novel Combination of Old Tactics
While the concept of an "evil maid attack"—physical tampering with an unattended device—has been around since at least 2009, the OVERCAST PANDA campaign introduced a new level of sophistication. CrowdStrike's Adam Meyers noted that the novelty lies in the combination of hotel room entry by a state intelligence service with direct malware deployment via bootable USB. This wasn't a dropped USB stick that the victim unknowingly plugs in; it was a direct injection of malware while the laptop was vulnerable.
The report indicates that the individuals gaining physical access were likely state actors or individuals coerced or bribed by state services, targeting executives at an agricultural conference – a sector aligned with China's strategic five-year plans. This suggests a highly targeted intelligence-gathering operation.
Why Old Security Measures Still Matter (and Are Often Ignored)
The ironic twist? The solutions to this type of attack aren't new or particularly complex. They involve leveraging existing firmware and policy settings:
- Disabling external boot in UEFI: Prevents booting from USB drives.
- BIOS administrator password: Secures BIOS settings and prevents unauthorized changes.
- Pre-boot authentication: Requires a PIN or key before the encrypted drive is accessible, even if booted from external media.
- Firmware monitoring: Detects any tampering with the device's firmware.
Meyers highlighted that these measures are "inconvenient solutions" that many organizations and individuals neglect. The difficulty often lies not in the technology, but in the organizational silos that prevent consistent implementation of these fundamental security practices across travel devices and corporate policies.
CrowdStrike's New Frontier: AI Security Amidst Evolving Threats
Interestingly, CrowdStrike disclosed this campaign shortly before announcing its new slate of AI security products, including Falcon Guardian and SafeMind, at its Fal.Con 2026 conference. While these advanced tools aim to combat the growing threat of AI-powered attacks and malicious AI agents, the OVERCAST PANDA incident serves as a stark reminder that even the most cutting-edge defenses can be rendered moot by a determined attacker exploiting basic physical vulnerabilities.
The report also points to the escalating threat landscape, with a 96% increase in registered CVEs in June 2026 alone and a surge in AI agent-triggered detections. However, Meyers emphasized that while AI-driven network attacks are concerning due to their scalability, the physical hotel room intrusions, though unscalable, are effective precisely because they bypass the digital defenses that budgets often prioritize.
Protecting Yourself on the Road
For travelers and executives, the advice is clear:
- Audit your devices: Ensure USB boot is disabled and BIOS settings are secured.
- Use full-disk encryption with pre-boot authentication: Don't rely solely on TPM-based BitLocker.
- Verify Secure Boot: Keep your system updated to prevent the use of compromised bootloaders.
- Issue dedicated travel devices: For international trips, use devices with limited access to production systems and no saved credentials.
As Meyers aptly put it, "If they can get their hands on it, they can own it." The security of your devices on the road often boils down to diligent configuration and a healthy dose of caution. The OVERCAST PANDA attack is a potent reminder that sometimes, the most effective security is the most inconvenient.
Can You find Now